Configuring Container umask Values in Docker
Context
Container umask configuration directly impacts file/directory permissions of newly created resources, affecting container security posture.
Symptom
Standard openEuler containers initialize with default umask 0027. After modification, the others group loses access permissions to newly created files/directories.

Possible Causes
The default umask was intentionally set to 0027 in runc implementation to enhance container security and mitigate potential attacks. This modification intentionally restricts others group access to new resources.
Solution
Option 1:
Modify Docker service configuration file /etc/sysconfig/docker:
Add --exec-opt native.umask=normal parameter to OPTIONS line, then restart dockerd:
systemctl restart docker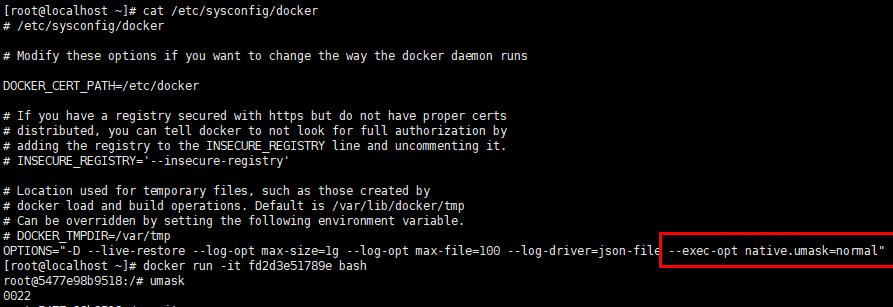
Option 2:
Include --annotation native.umask=normal parameter when executing docker run|exec commands:
docker run --annotation native.umask=normal XXX
docker exec --annotation native.umask=normal XXX
Licensed under the MulanPSL2
 J.G.W.A.B. No. 11030102011597